Enterprise Network Security Solutions combine policies, technologies, and operational practices to protect an organization’s users, devices, applications, and information. Organizations face more than one route into their systems, from on-site servers to cloud services and remote work. A single weak point can expose sensitive data, including customer data, or allow unauthorized access. Defense in depth means using complementary physical, technical, and administrative safeguards so one control’s failure does not leave an organization unprotected. This layered approach helps preserve confidentiality, integrity, and availability while supporting day-to-day business. We offer practical guidance for organizations that need safeguards to work across on-premises, cloud, and remote-work environments. A coordinated set of controls gives security teams a stronger foundation than any single safeguard.
Key Takeaways
- Protect users, devices, applications, and information together.
- Use safeguards that support confidentiality, integrity, and availability.
- Match controls to on-premises, cloud, and remote-work needs.
- Limit access to the systems and data each person needs.
- Plan to spot threats, respond, and restore services.
What Does Enterprise Network Security Protect?
A compromised account or exposed server can put data, operations, and customer trust at risk at the same time. Enterprise network security protects the confidentiality of private information, its integrity, and its availability when people need it. A breach can disrupt business even when attackers do not steal data.
A breach can expose information, change it, or keep people from using it.
Confidentiality means only approved people can see information. Integrity means information stays accurate, and availability means systems remain usable. Threats can harm all three, expose customer data, interrupt services, and damage an organization’s reputation.
Cyberattacks have more than doubled in the past four years, and about 2,200 occur each day, or one every 39 seconds. These figures describe broad risk, not the odds for a single organization.
The average time to contain a data breach is 277 days. CVEs, or published records of known software flaws, rose about 30% from 2023 to 2024.
The 2025 global average breach cost was $4.44 million. In the United States, the average was $10.22 million, up 9% year over year, as reported in the IBM 2025 breach-cost figures.
Ransomware can move faster than a long response timeline suggests. Fog ransomware emerged in May 2024 and could encrypt files and steal data in as little as two hours.
A rapid incident can still take hours to unfold, as the May 2024 Fog ransomware example demonstrates.
Enterprise Network Security Solutions: Which Layers Belong in the Architecture?
A resilient architecture combines traffic controls, identity checks, device safeguards, and data protection rather than relying on a single perimeter. Each layer covers a different path into the enterprise network, so one missed control does not expose every system. Network segmentation and least-privilege access help limit an attacker’s reach.
How Firewalls and Segmentation Control Traffic
Firewalls inspect network traffic and allow or block it under set rules. A next-generation firewall (NGFW) can apply added security checks alongside traffic filtering.
Network segmentation and subnetting divide a network into smaller zones. If an attacker enters one zone, those boundaries can limit lateral movement to other devices and data.
How Identity and Remote Access Controls Limit Entry
Identity controls check who a user is and what that person may reach. Multi-factor authentication (MFA) asks for more than a password, which makes stolen credentials less useful.
A remote-access virtual private network (VPN) encrypts traffic through a tunnel between a user and the network. Zero trust network access (ZTNA) instead grants identity-based access to specific applications, without implicit trust in the user or device.
Both can support remote work, but they grant different kinds of access. A VPN may connect a user to a broader network, while ZTNA limits access to approved applications.
How Data and Endpoints Need Separate Safeguards
Encryption protects data from being read without the right key, both in transit and at rest. Endpoint protection checks laptops, servers, and other devices for harmful activity.
Data loss prevention (DLP) policies can flag or block sensitive data as it moves through email, cloud services, or removable media. These controls add protection beyond network boundaries.
WPA2 wireless security uses AES encryption to protect a wireless connection. It does not protect every part of an enterprise network, so wired systems and cloud access need their own controls.
Map sensitive data flows and access paths first, then apply controls at the boundaries that matter most.
Which Network Security Tools Work Together?
A firewall can block disallowed traffic, while detection tools help identify activity that has already crossed a boundary. Prevention and detection play different roles, and teams need both to spot and handle threats. Connect each alert to an owner who can act on it.
What Firewalls and IDPS Prevent
A firewall filters traffic against rules. An intrusion detection and prevention system (IDPS) can detect suspicious activity, raise alerts, or block traffic when deployed inline.
IDPS types include network-based, host-based, wireless, and network behavior analysis systems. A web application firewall focuses on web applications and can help mitigate distributed denial-of-service (DDoS) and SQL injection attacks.
How NDR and SIEM Improve Detection
Network detection and response (NDR) looks for unusual behavior in network activity. It can help security teams investigate activity that ordinary rules may not flag.
Security information and event management (SIEM) brings logs, alerts, threat data, and risk information together. This gives teams a shared view across systems, but staff still need to review findings and respond.
| Tool | Main job | Typical signal or action | Where it fits |
|---|---|---|---|
| NGFW | Filter traffic and apply security checks | Blocks traffic that breaks policy | Network boundary or cloud edge |
| IDPS | Detect or block suspicious activity | Alerts or stops a known pattern | Network, host, or wireless link |
| NDR | Find unusual network behavior | Flags a change in traffic patterns | Internal network monitoring |
| SIEM | Bring security events together | Correlates logs and alerts | Central security operations |
When VPNs, NAC, and DLP Add Controls
A VPN encrypts remote traffic, while network access control (NAC) checks whether a device meets admission rules. DLP helps control sensitive data movement, such as a file sent to an unapproved service.
These tools address separate risks. A secure remote connection does not prove that a device is safe, and device checks do not stop every data leak.
Connect alerting tools to a defined response owner so a detected threat does not remain an unattended notification.
What Network Security Best Practices Reduce Risk?
The most useful security practices are repeatable controls that reduce unnecessary access and make suspicious activity easier to spot. Small routines can close gaps before attackers find them. Use several layers, then test whether each one works.
Build Defense in Depth and Limit Access
Give each user only the access needed for current work, and review rights when roles change. Network segmentation and ZTNA can reduce broad access and help limit lateral movement.
Require MFA for important accounts, enforce written security policies, and train staff to spot common threats. Human error played a role in 88% of cyber incidents, so clear procedures matter.
Verizon recorded 22,052 incidents across 139 countries in 2024. That scale supports routine staff awareness, not blame after a mistake.
Monitor, Practice, and Recover
Use continuous monitoring to review activity and route urgent alerts to a person who can respond. Practice incident response so staff know who makes decisions and how they share updates.
Backups and data redundancy support recovery after an incident. Test that teams can restore key systems, not just that backup jobs completed.
Security automation was associated with $2.22 million in savings per breach. At the same time, the cybersecurity workforce gap reached about 4.8 million, up 19% year over year; severe staffing shortages added $1.76 million to average breach costs.
- Review access rights.
- Patch exposed systems.
- Test backups.
- Rehearse incident response.
- Review alerts for coverage gaps.
Automation can help teams handle routine work, but it cannot replace human oversight or a clear response plan. Test a recovery plan with a real restoration exercise, not just a check that backup files exist.
How Should We Choose a Network Security Provider?
Start by matching a provider’s controls and operating model to the risks and systems your organization actually has. Fit matters more than a broad feature list. Compare coverage, deployment, integration, reporting, and support before choosing.
Cybersecurity companies may serve different needs, from cloud workloads to branch offices and remote users. Compare each provider against your own use cases rather than expecting one universal winner.
Check whether the security solutions work with your identity tools and logging systems. Ask how teams receive reports, who handles urgent support, and how the service can scale as your enterprise changes.
NIST Cybersecurity Framework 2.0 helps organizations understand, assess, prioritize, and communicate cybersecurity risks. Its six functions are Govern, Identify, Protect, Detect, Respond, and Recover.
The NIST Cybersecurity Framework 2.0 outlines outcomes without requiring one specific way to achieve them. ISO/IEC 27001 is an information security management standard that can guide questions about policies and oversight.
- Coverage: Which users, devices, applications, and networks are protected?
- Deployment: Does it support on-premises, cloud, and hybrid needs?
- Integration: Can it use existing identity and logging systems?
- Compliance reporting: Can it show controls and gaps clearly?
- Support: Who responds, and when is help available?
Ask for a demonstration using a representative workflow, such as investigating a suspicious login across identity and endpoint logs.
What Do Enterprise Firewall Market Trends Mean for Buyers?
Enterprise firewall investment is growing, but the useful choice for an organization depends on where its users, applications, and traffic reside. Growth shows demand for protection across cloud and hybrid infrastructure, not proof that a specific product fits. Match deployment to the systems and traffic your team must secure.
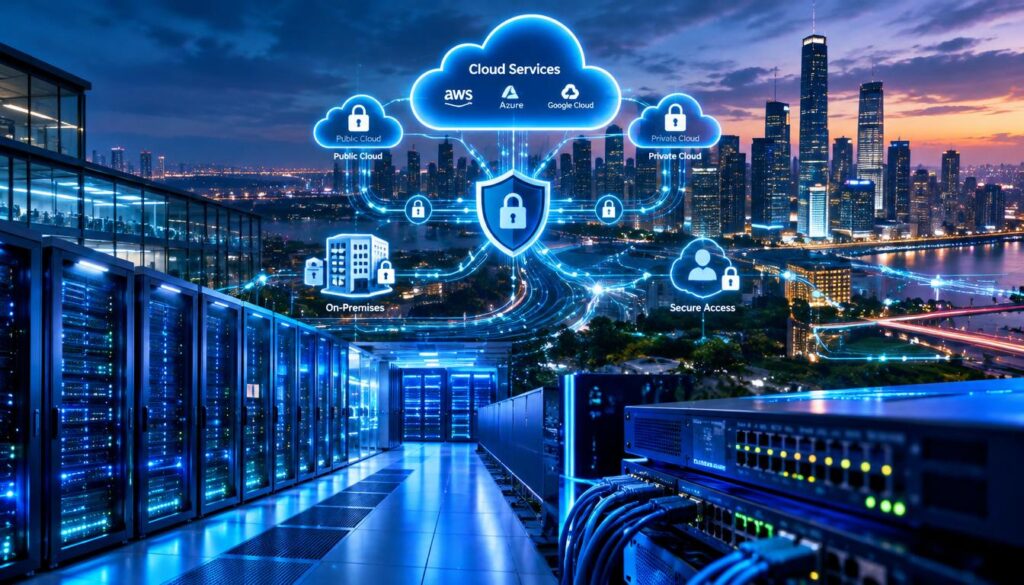
The global enterprise firewall market was estimated at $15.8 billion in 2025. It is projected to reach $42.6 billion by 2035, with a 10.4% annual growth rate from 2026 through 2035.
North America is expected to generate the most revenue from 2026 through 2035, while Asia-Pacific is expected to grow significantly. The global network security market is valued at $27.11 billion and projected to reach $79.29 billion by 2033.
Security solutions account for 72.6% of network security market revenue. Secure Access Service Edge (SASE) is growing at nearly 29% each year, as cloud-delivered security gains use.
| Deployment | Where controls run | Typical fit | Main consideration |
|---|---|---|---|
| On-premises | Appliances at company sites | Local data centers and offices | Hardware needs local care |
| Cloud-based | Cloud service provider locations | Cloud apps and remote users | Match controls to each cloud |
| Hybrid | Sites and cloud environments | Mixed local and cloud systems | Keep policies and visibility aligned |
Product types include NGFW, unified threat management (UTM), traditional firewalls, and web application firewalls. Each type addresses different traffic and control needs.
SASE combines network access and security services delivered through the cloud. Firewall-as-a-Service (FWaaS) offers firewall controls as a cloud service, rather than relying only on appliances at each site.
Market growth is context for planning, not a buying rule. Treat market growth as context for planning, then evaluate each option against your own deployment and control requirements.
How Do Cloud Security and AI Change Network Defense?
Cloud and AI workloads add changing assets and data flows that perimeter-only controls may not cover. Cloud-native security follows applications, data, and infrastructure across hybrid and multicloud settings. Teams still need to manage risks shared across cloud services and their own workloads.
What Cloud-Native Security Covers
A cloud-native application protection platform (CNAPP) brings security controls together for cloud applications, data, and infrastructure. Palo Alto cloud network security includes coverage across hybrid and multicloud environments, with controls for risks that perimeter tools may miss.
Cloud providers and customers share responsibility. Providers secure parts of the cloud service, while organizations must also protect their applications, data, access, and settings.
How Prisma Cloud Supports Code-to-Cloud Security
Prisma Cloud is a software-as-a-service CNAPP for applications, data, and infrastructure across hybrid and multicloud environments. Its code-to-cloud coverage can include infrastructure as code (IaC), CI/CD pipelines, secrets, software composition analysis, and cloud security posture management.
It also supports API visibility, cloud infrastructure entitlement management, workload scanning, threat detection, serverless, host, and web application and API security. Other documented capabilities include compliance management, IaC misconfiguration detection, vulnerability scanning, and least-privileged access enforcement.
Prisma Cloud analyzes one trillion events every 24 hours, while Prisma Cloud Precision AI detects 1.5 million new attacks each day. Prisma Cloud Copilot conversationally analyzes code-to-cloud data to help investigate and address cloud risks.
What Prisma AIRS Adds for AI Applications and Agents
Prisma Cloud AI security extends to AI applications and agents through Prisma AIRS. It can discover AI apps and agents, assess risk, protect interactions in real time, and govern agents.
Its named capabilities include AI Gateway, AI Supply Chain Security, AI Red Teaming, AI Runtime Security, AI Posture Management, Agent Identity Security, and Agentic Endpoint Security.
Runtime security monitors AI behavior and applies safeguards against manipulation, data exposure, and unsafe actions. Network Intercept and API Intercept are two deployment modes.
IDC projects a 40-fold rise in enterprise AI agents by 2029 and says 70% of developers will work alongside autonomous agents by 2030. A SonarSource survey found 42% of code developers commit is AI-generated or AI-assisted.
Validate AI security controls against the model, agent, and data flows the organization actually uses.
Which Enterprise Platforms Fit Different Network Environments?
A platform is a better fit when its deployment choices and controls match the organization’s actual network boundaries and operating model. Check the operating details, not just product names. Compare deployment, policy management, and response in the same table.
What Strata Offers Across Deployment Types
Palo Alto Networks’ Strata Network Security Platform uses a hybrid mesh firewall model across hardware, virtual, cloud-native, and Firewall-as-a-Service deployments. It is designed to protect users, applications, and devices in different locations through shared policy and management.
Strata NGFW App-ID identifies applications regardless of port, protocol, or encryption level. The firewall is available as hardware appliances, virtual machines, and cloud-native deployments.
Panorama centrally manages on-premises deployments. Strata Cloud Manager provides cloud-based management for NGFW and SASE environments, giving teams different options for managing network security.
How Check Point and Fortinet Address Firewall Needs
Check Point NGFW uses ThreatCloud AI, which aggregates telemetry from more than 150,000 connected networks and over 50 AI engines. It delivers protective updates worldwide in under two seconds after new threats are detected.
In independent Miercom benchmark testing, Check Point NGFW achieved a 99.9% malware block rate and a 99.7% phishing and malicious URL block rate. FortiGate supports data center, campus, branch, and small-office deployments.
| Platform | Deployment or coverage | Notable capability | Management or response |
|---|---|---|---|
| Palo Alto Networks Strata | Hardware, virtual, cloud-native, FWaaS | App-ID identifies applications | Panorama or Strata Cloud Manager |
| Check Point NGFW | Enterprise firewall deployments | ThreatCloud AI shares threat updates | Updates follow new threat detection |
| Fortinet FortiGate | Data center, campus, branch, small office | Supports varied site sizes | Deployment spans local network settings |
| Cisco Secure Firewall | Physical, virtual, and cloud | Integrates Talos threat intelligence | Supports multiple firewall forms |
| Zscaler Zero Trust Exchange | Access to specific applications | Uses identity, context, and policy | Brokers application access |
Other enterprise firewall companies include Juniper Networks, SonicWall, Sophos, WatchGuard, Barracuda Networks, Forcepoint, Huawei, Hillstone Networks, Sangfor, and Netskope. This list also includes A10 Networks, Versa Networks, and McAfee Enterprise; it does not rank them.
When Email and Identity Signals Need to Join Network Data
Cortex Advanced Email Security uses large language models, behavioral analytics, and user profiling to review message content and intent for phishing signs.
It correlates email, identity, and endpoint data through Cortex XDL. It can remove malicious emails, disable compromised accounts, and isolate endpoints in real time.
Confirm which management consoles and policies teams will operate before standardizing on a platform.
How Do We Test and Improve Network Security?
A firewall’s rated throughput is not enough to show how it will perform with the protections an organization plans to run. Test the real policy load, not a bare device. Run security and performance checks with the same protections enabled.
A bare-firewall speed test does not show the cost of running real security checks.
A security test checks whether controls find or block attacks. A performance test measures speed and capacity under load; both matter, but they answer different questions.
- Inventory assets and identify their owners.
- Review traffic and access policies.
- Scan for vulnerabilities.
- Test detection and response.
- Record remediation owners and deadlines.
Nmap can help find hosts, open ports, services, and operating systems. Wireshark captures and inspects network packets, which helps teams examine traffic at the packet level.
Realistic firewall testing measures Threat Prevention Throughput with IPS, antivirus, and SSL inspection enabled at the same time. Include TLS 1.3 inspection and full security profiles.
TLS decryption can cut throughput by 50%-80% on older appliances as operations scale. Testing without inspection may overstate the speed teams will see in production.
Re-test after policy or traffic changes, and track both prevention outcomes and throughput under the same security profile.
Conclusion
Strong enterprise protection comes from controls that work together and are tested against the organization’s real environment. Prevention, detection, access control, monitoring, and recovery each support a different part of the response.
Start with an inventory of assets and data flows, then rank gaps by business risk. That helps teams direct limited time toward the systems and information with the greatest impact.
Start by documenting your most sensitive data flows and the systems that can reach them, then assign an owner to each gap you uncover.